Panchan's Mining Island [Guest Diary]
by Zachary Norwood, SANS.edu BACS Student (Version: 1)
[This is a Guest Diary by Zachary Norwood, an ISC intern as part of the SANS.edu BACS program]
Crypto mining malware has been active and spreading across the internet for quite some time now. Moreover, the DShield honeypot picked up a worm that self-propagates through a plethora of means. One of them is stealing SSH keys after it gains access to a system. Furthermore, it also leverages a rootkit to maintain access to infected systems. One would hope that threat actors would have moved on past this worm by now. However, due to its rudimentary design and its effectiveness, they have had no reason to move on.
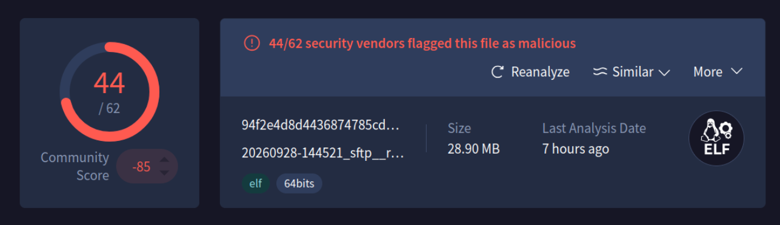
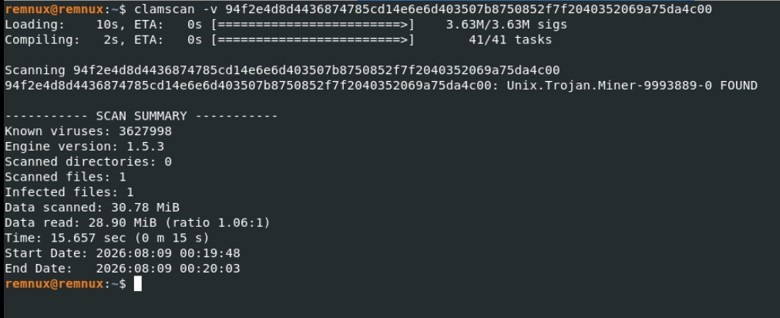
A malicious binary was uploaded and executed on the DShield honeypot, and that is where a copy of the Panchan worm was obtained. It is written with Golang, and it is a peer-to-peer botnet. Moreover, this worm was first identified in 2022. Many vendors recognize this worm now as seen below.
VirusTotal
Clamscan
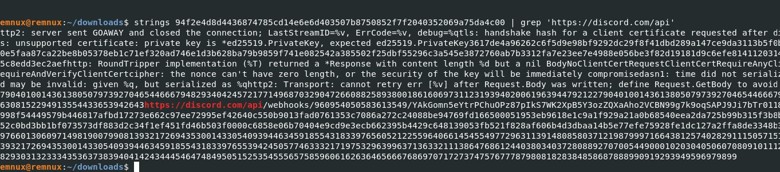
Therefore, a system with security controls such as egress filtering, ingress filtering, access control lists, continuous monitoring, and passwordless authentication will prevent this worm from taking root. However, many systems are insecure and unpatched. This is why this worm is still propagating across the internet. The strings captured from the binary below show how simple it is to find its command-and-control channel and the functions that it consists of.
Furthermore, leveraging something as simple as syslog to pull logs and using commands such as grep to find privilege escalation activities, software installation, software removal, and access to ports such as SSH will allow an analyst to identify this activity. However, this does not scale well. Therefore, leveraging a SIEM to gather and parse this data is a much more effective solution. Next, all traffic entering and exiting from both the trusted and untrusted networks needs to pass through at least one firewall. Preferably, also having an intrusion detection or prevention system right after the public facing firewall in the trusted zone.
Command and Control Channel
Panchan Functions
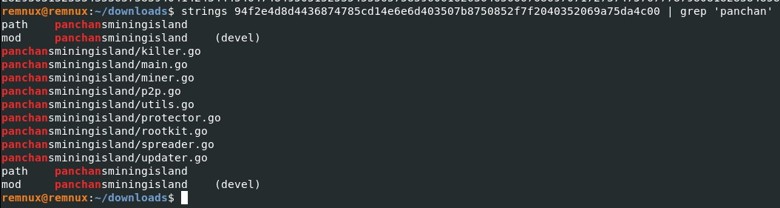
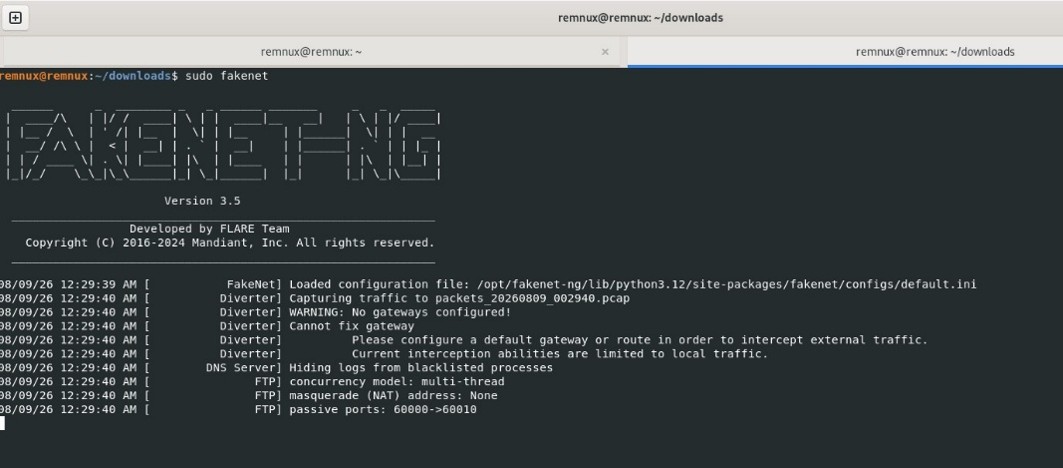
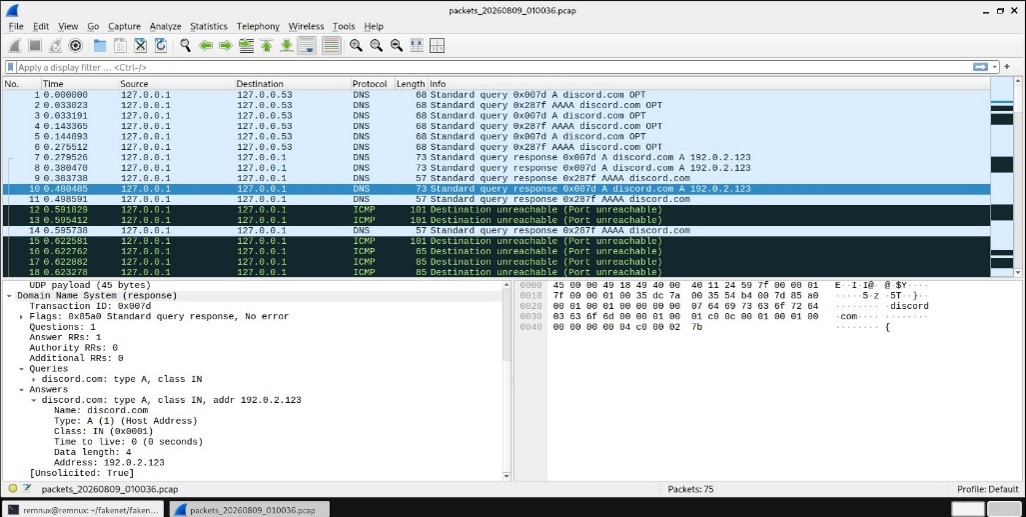
These captures clearly show the source files that the Panchan worm consists of. To dig deeper into what this binary can do, a network simulator was used. Moreover, the specific network simulator that was used was FakeNet-NG with Wireshark to intercept the network traffic. These tools were used to identify what URL it was reaching out to once it was installed on a system. FakeNet-NG is a tool developed by the Mandiant FLARE team for dynamic network analysis. This tool simulates legitimate network traffic, allowing an analyst to identify how the malware interacts with the network and if it is communicating with an external server. This specific strain of this worm was using a discord channel as a command-and-control server. This was identified by capturing and dissecting the network traffic that was generated by the worm interacting with the FakeNet-NG network.
FAKENET-NG
Wireshark Capture
Panchan, the peer-to-peer crypto mining worm, is a threat to any organization who has internet facing servers. This worm is mainly a threat to insecure systems, and opening SSH to a public network needs to be done in a secure way. Fail2Ban is a service that scans log files for repeated failed login attempts. This service then blocks that IP address by updating the system’s firewall rule. Fail2Ban is another control that should be put in place with a public facing SSH port. Services like SSH should have multi-factor authentication, and an access control list. The access control list should include specific IP addresses or a jump box. Disabling root login with SSH is another essential security control that needs to be implemented.
With SSH, public and private key pairs are another option for authentication. This will then create the capability to disable password authentication for the SSH service preventing brute force attacks. However, these key pairs are often created and forgotten about. This is a security concern, and SSH private keys are something that this worm is designed to steal. Once it has stolen a private key, it attempts to pivot to hosts in the running user’s SSH known_hosts file. A simple mitigation to protect the data within the known_hosts file is to use the HashKnownHosts option within a systems SSH configuration. Furthermore, it is best to mitigate long lived credentials and SSH key stealing by leveraging tools likeHashiCorp Vault to sign SSH certificates with short expirations. This ensures that reusing a key becomes highly impractical or even impossible. The user will authenticate to Vault with their credentials then they send their SSH public key to Vault for signing, and finally Vault then signs the SSH key. Then it returns the SSH certificate to the user. This certificate can be used to log in to any host configured to trust the Vault CA. Leveraging such infrastructure will also allow an organization to disable password authentication entirely for services like SSH.
Furthermore, leveraging something as simple as syslog to pull logs and using commands such as grep to find privilege escalation activities, software installation, software removal, and access to ports such as SSH will allow an analyst to identify this activity. However, this does not scale well. Therefore, leveraging a SIEM to gather and parse this data is a much more effective solution. Next, all traffic entering and exiting from both the trusted and untrusted networks needs to pass through at least one firewall. Preferably, also having an intrusion detection or prevention system right after the public facing firewall in the trusted zone.
Typical indicators of compromise for this worm include multiple failed authentication attempts via SSH, unusual resource usage on infected systems, and processes that cannot be killed by any means. This worm also creates hidden directories in the running users home directory or folders like /tmp. Often, these directories have names that are strings that have high amounts of entropy. For this strain of this worm, servers reaching out to services like Discord on a regular basis is another indicator of compromise that an analyst can look for. In conclusion, denying by default and allowing by exception is a vital strategy for systems facing untrusted networks. These same techniques that were discussed above can be used to protect critical public facing infrastructure from threat actors.
[1] https://github.com/mandiant/GoReSym
[2] https://github.com/mandiant/flare-fakenet-ng
[3] https://www.akamai.com/blog/security-research/new-p2p-botnet-panchan
[4] https://www.akamai.com/blog/security-research/cryptominer-anatomy-internals
[5] https://attack.mitre.org/
[6] https://developer.hashicorp.com/vault/docs/secrets/ssh/signed-ssh-certificates
[7] https://www.hashicorp.com/en/blog/managing-ssh-access-at-scale-with-hashicorp-vault
[8] https://github.com/bruneaug/DShield-SIEM/tree/main
[9] https://www.sans.edu/cyber-security-programs/bachelors-degree/
-----------
Guy Bruneau IPSS Inc.
My GitHub Page
Twitter: GuyBruneau
gbruneau at isc dot sans dot edu
Orphaned VBA Projects Inside DWG Files
Years ago I wrote diary entries about VBA code stored inside AutoCAD drawing files (.dwg).
In a nutshell: the VBA code is stored inside an OLE file, that is embedded inside the DWG file. You can do a brute-force search for the embedded OLE file, or you can follow a pointer inside the header of the DWG file.
I wrote a small Python script (autocad.py) for this second case. It looks at a 32-bit pointer at position 0x24 inside the DWG file. This points to a 16-byte long header, followed by the embedded file. This 16-byte long header contains the length of the embedded file. You use the script together with my tool cut-bytes.py, like this:
cut-bytes.py -S autocad.py -P AutoCAD : 461ed52aeb75384133a8238b2eb481ae5d505d4961effa622673d65a889c8218.vir.zip | oledump.py
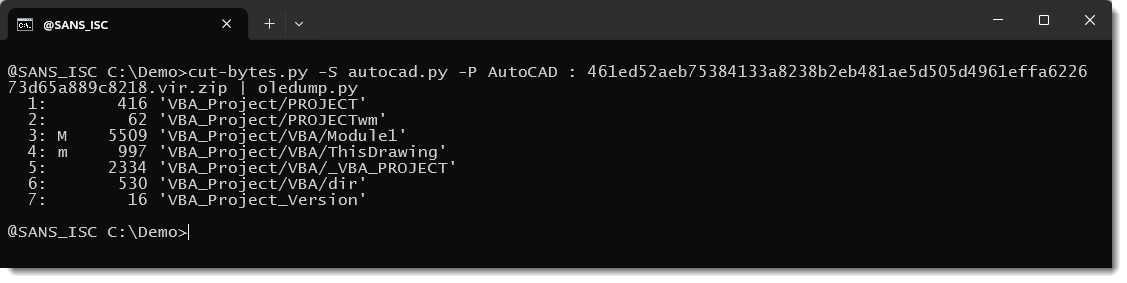
This command carves the DWG file (inside the ZIP file) and extracts the embedded OLE file, and pipes it into oledump.py for analysis.
When the pointer is zero, there is no embedded OLE file, and cut-bytes.py returns nothing.
Recently, I discovered 2 DWG files that are an exception: their pointer to the embedded OLE file is zero, but if you do a brute-force search, you will find an embedded OLE file with a VBA project.
For example this DWG file.
Its pointer to the embedded VBA project is zero:
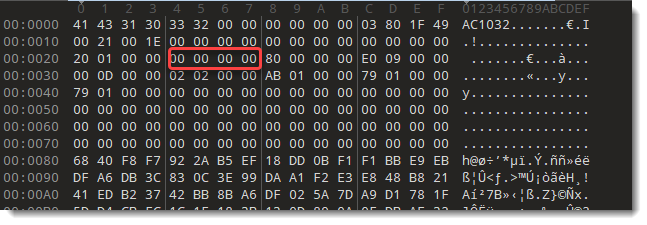
But it contains an embedded OLE file:
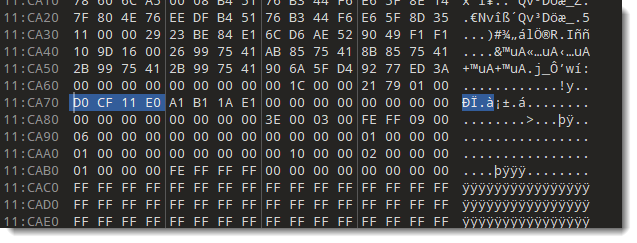
And right in front of the embedded OLE file, there is the 16-byte long header that contains the lenght of the embedded file.
Using the AutoCAD script to extract the file gives nothing:
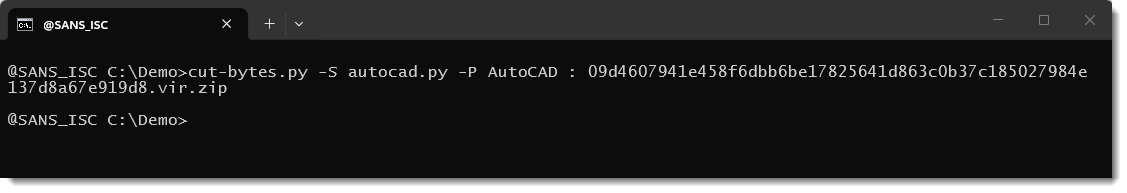
But oledump.py can find the embedded OLE file and analyze it:
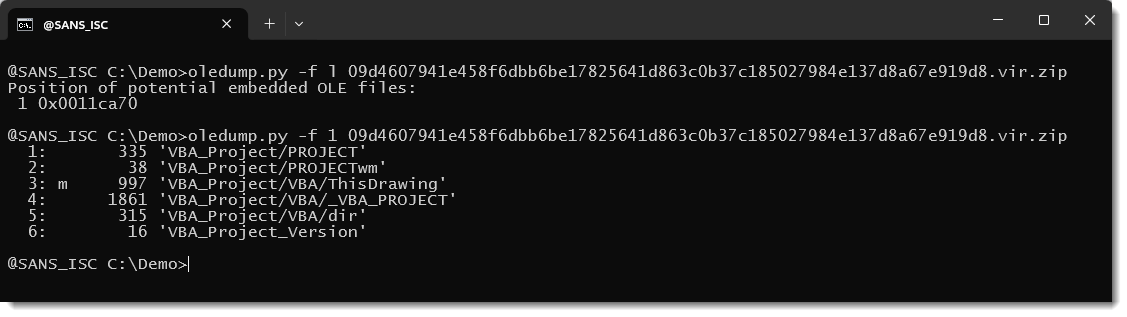
So while using oledump.py to analyze DWG files you find a VBA project embedded inside a DWG file, then also verify if it is not orphaned: verify that the pointer at 0x24 is not zero (or use the autocad.py script).
Because when a DWG file contains an orphaned VBA project, the VBA code can not have executed when someone opened the DWG file with AutoCAD. AutoCAD "does not see" orphaned VBA projects.
Notice that a default installation of AutoCAD does not support VBA. VBA for AutoCAD is a separate install.
I don't know how orphaning happens, but I did find an AutoLISP command to remove a VBA project from a DWG file:
(dictremove (namedobjdict) "ACAD_VBA")
Maybe this dictremove command clears the pointer, but does not remove the embedded OLE file.
Didier Stevens
Senior handler
blog.DidierStevens.com

Comments